 D365 Finance
19 min
Cybersecurity requires more than installing antivirus software or responding to threats after an incident. As your business adopts cloud applications, remote work, connected devices, and shared data, security must evolve alongside your technology environment.
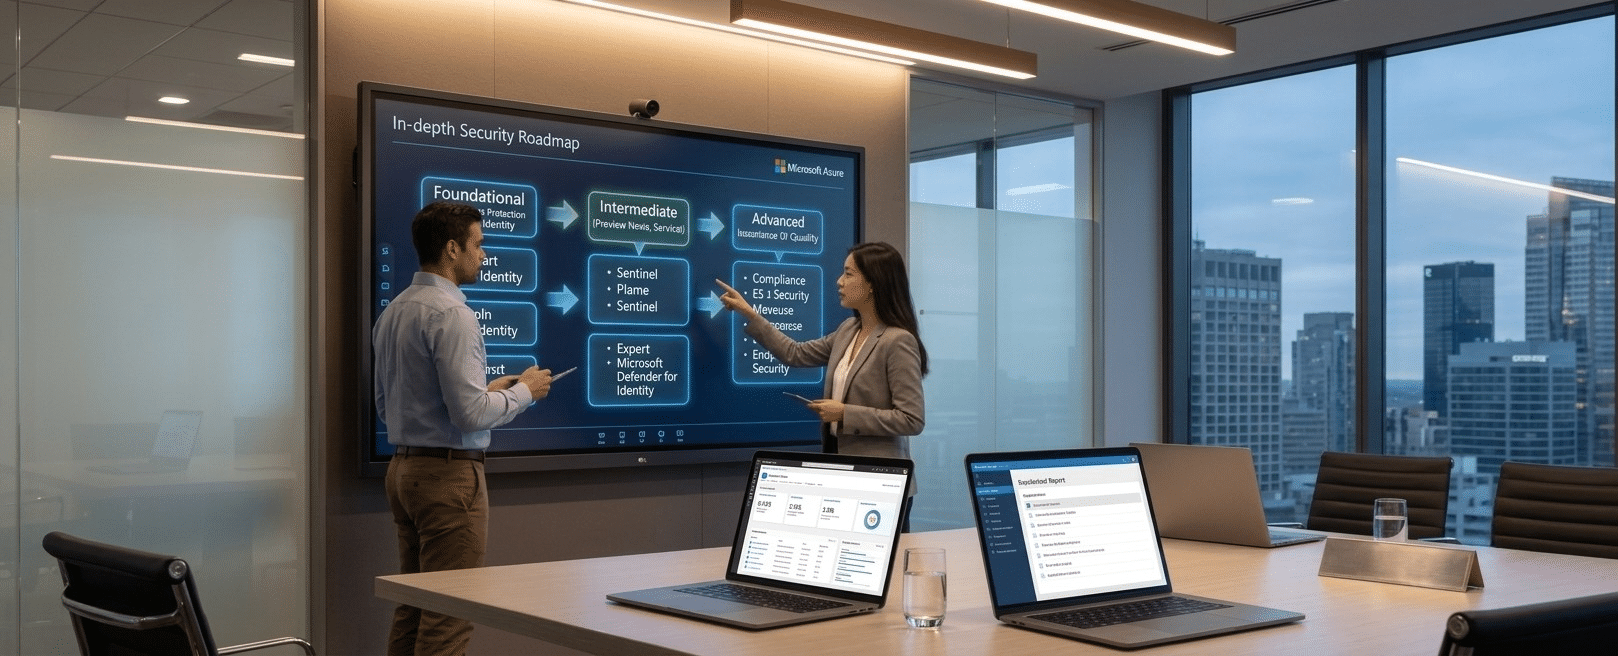
A Microsoft security roadmap provides a structured approach to reducing cyber risk, improving security maturity, and selecting the right protection tools while supporting business growth over time.
Microsoft provides several security technologies that work across identities, devices, applications, email, and cloud environments. However, purchasing multiple products does not automatically create a secure workplace. You need to understand your current risks, identify gaps, and decide which controls should receive attention first.
What Is a Microsoft Security Roadmap?
A security roadmap is a planned sequence of activities designed to improve your organization’s protection against cyber threats while supporting compliance requirements, operational resilience, and long-term risk reduction.
It connects security goals with technology, people, policies, and measurable results.
For a Microsoft based organization, this plan may include Microsoft Entra ID, Microsoft Defender, Microsoft Sentinel, Microsoft Intune, and Microsoft Purview. Each technology addresses different security requirements, so your selection should reflect your environment.
For example, a business with employees working from different locations may prioritize identity protection and device security. An organization handling sensitive customer information may need stronger data classification, access controls, and monitoring.
The roadmap should also define ownership. Your IT team, security administrators, department managers, and leadership should understand their responsibilities.
Step 1: Assess Your Existing Security Environment
Before introducing new tools, examine the systems and controls already in place. An assessment helps you understand where protection is working and where improvements are needed.
Start by reviewing user accounts, administrator privileges, employee devices, Microsoft 365 settings, cloud resources, and third party applications. Check whether former employees still have active accounts and whether users receive more permissions than their roles require.
You should also review existing security incidents, backup procedures, software updates, and access policies. These details help identify weaknesses that may not be visible from a product dashboard.
Document your findings in a risk register. Record each issue, its possible business impact, its priority, and the person responsible for addressing it. This creates a practical starting point for your Microsoft security roadmap.
Step 2: Strengthen Identity and Access Management
Compromised credentials remain a major concern for organizations. An attacker who gains access to a valid account may attempt to reach email, business applications, files, or administrative systems.
Microsoft Entra ID provides identity and access management capabilities for Microsoft cloud environments. You can use it to manage authentication, user access, and security policies.
Begin with multifactor authentication (MFA). Require additional verification when users sign in, particularly for accounts with access to sensitive information. Consider passwordless authentication where it fits your security requirements and aligns with your broader Zero Trust security strategy.
Conditional Access policies can evaluate signals such as user identity, device status, location, and application access before allowing a sign in. Use these policies carefully and test them before broad deployment to avoid disrupting legitimate work.
Review administrator accounts separately. Limit privileged access, remove unnecessary permissions, and monitor important administrative activity.
Step 3: Protect Devices with Microsoft Defender and Intune
Employees may access company information through office computers, laptops, mobile devices, and remote workstations. Every connected endpoint can introduce security risks if it lacks suitable protection.
Microsoft Defender for Endpoint provides endpoint security capabilities, including threat detection, investigation, and response. It can help security teams identify suspicious behavior and respond to endpoint threats.
Microsoft Intune supports device management and security policy enforcement. Organizations can use it to configure supported devices, apply compliance requirements, and manage access to company resources.
Your device security plan should cover:
- Operating system and application updates.
- Endpoint protection and threat monitoring.
- Device encryption where supported.
- Screen lock and authentication requirements.
- Lost or stolen device procedures.
- Access restrictions for devices that do not meet company policies.
Do not assume that every employee device needs the same configuration. Establish policies based on device ownership, business use, information sensitivity, and operational needs.
Step 4: Secure Email, Collaboration, and Business Data
Email and collaboration platforms often contain sensitive business information. Employees exchange contracts, financial documents, customer records, and internal files through these channels.
Microsoft Defender for Office 365 provides protection against threats such as phishing, malicious links, and harmful attachments, depending on the selected plan and configuration. Review its available protection policies and make sure they match your organization’s email risks.
Data protection requires separate attention. Microsoft Purview provides capabilities for data classification, sensitivity labels, data loss prevention, and information governance, subject to licensing and configuration.
Start by identifying the information your business must protect. Customer details, employee records, financial documents, and intellectual property may require different access and handling rules.
Train employees to recognize suspicious messages and report unusual activity. Technical controls are important, but informed users also play a major role in reducing security incidents.
Step 5: Monitor Threats with Microsoft Sentinel
Preventive controls cannot stop every attack. Your organization also needs a way to identify suspicious activity and investigate incidents.
Microsoft Sentinel is a cloud-native security information and event management (SIEM) and security orchestration, automation, and response (SOAR) platform. It can collect security data from supported sources, correlate events, automate investigation workflows, and help security teams investigate potential threats more efficiently.
You can connect relevant Microsoft services and other supported systems to improve visibility across your environment. Detection rules and analytics help identify patterns that may indicate suspicious behavior.
Begin with the systems that matter most. Monitor identity activity, endpoint alerts, cloud resources, and important administrative events. Define who reviews alerts and how incidents should be escalated.
A monitoring platform is useful only when someone acts on its findings. Establish response procedures, assign responsibilities, and test the process through realistic incident exercises.
Step 6: Create a Phased Implementation Plan
Trying to introduce every security control at once can place pressure on IT teams and disrupt employees. A phased approach makes the work easier to manage.
Your roadmap can follow a practical sequence:
First 30 days: Assess the environment, review administrator access, identify critical assets, and address urgent security gaps.
Days 31 to 60: Strengthen authentication, review Conditional Access, improve endpoint policies, and check email protection settings.
Days 61 to 90: Expand monitoring, improve data protection, document incident response procedures, and begin employee awareness activities.
These timeframes are planning examples, not fixed implementation requirements. Your actual schedule will depend on system complexity, licensing, available staff, and existing security maturity.
Measure progress using relevant indicators such as multifactor authentication coverage, device compliance, unresolved high priority alerts, and incident response time.
How Cambay Solutions Can Help Build Your Security Roadmap
Selecting Microsoft security products is only one part of improving protection. You also need to understand how the tools fit together, which risks matter most, and how security changes affect daily business operations.
Cambay Solutions provides Microsoft focused services across security and compliance, Azure, Microsoft 365, Defender, Sentinel, and related technologies. These capabilities can support organizations planning improvements to their Microsoft security environment.
A structured engagement may include reviewing existing configurations, identifying security gaps, planning identity and endpoint controls, assessing cloud protection requirements, and defining monitoring and response processes.
When evaluating Microsoft security roadmap consulting support, ask how the provider assesses risks, handles licensing requirements, tests policy changes, documents configurations, and supports your team after implementation. Also request clear project responsibilities and measurable outcomes.
The objective is to build security controls that protect business information without creating unnecessary obstacles for employees.
Frequently Asked Questions
- What is a Microsoft security roadmap?
It is a planned approach to improving cybersecurity using Microsoft technologies, security policies, risk assessments, and ongoing monitoring.
- Which Microsoft tools are used for cybersecurity?
Common tools include Microsoft Entra ID, Microsoft Defender, Microsoft Sentinel, Microsoft Intune, and Microsoft Purview. The right combination depends on your requirements and licensing.
- Is Microsoft Defender enough to protect a business?
Defender provides important security capabilities, but no single product covers every risk. Businesses also need identity protection, device management, data controls, monitoring, and incident response procedures.
- What is the role of Microsoft Sentinel?
Microsoft Sentinel helps collect and analyze security information from connected systems so security teams can detect, investigate, and respond to potential threats.
- How often should a security roadmap be reviewed?
Review it at least annually and whenever major changes occur, such as cloud migrations, new applications, business expansion, or significant security incidents.
- Does a Microsoft security roadmap require new licenses?
Not always. Some organizations may already have access to relevant capabilities through existing subscriptions. Review current licensing and feature availability before purchasing additional products.
- Can a business implement Microsoft security tools in phases?
Yes. A phased rollout allows you to address urgent risks first, test policies, train employees, and expand protection according to business priorities.