 Dynamics 365 F&SCM
13 min
Why a Microsoft Security Assessment Matters
Cybersecurity is no longer limited to protecting a company network from external threats. Modern organizations depend on cloud applications, remote access, employee devices, business applications, data platforms, and third party services. A microsoft security assessment helps organizations examine how their Microsoft environment is configured, where security gaps may exist, and which areas should receive attention before a security incident exposes a weakness.
For many businesses, the challenge is not the lack of security tools. Microsoft environments can include Microsoft 365, Azure, Microsoft Entra ID, Defender, Intune, Sentinel, SharePoint, Teams, and other services. The challenge is understanding how these technologies work together and whether security controls are configured according to the organization’s actual requirements. An assessment provides a structured way to examine that environment.
What Is a Microsoft Security Assessment?
A Microsoft security assessment is a structured review of security controls, configurations, identities, devices, applications, data, and operational practices within a Microsoft technology environment. The exact scope depends on the organization, the services it uses, its industry requirements, and the objectives of the assessment.
The purpose is not simply to identify technical weaknesses. A useful assessment should help an organization understand which findings create the greatest business risk and what should be done about them. Some issues may require immediate attention, while others may be lower priority improvements that can be addressed through a longer security roadmap.
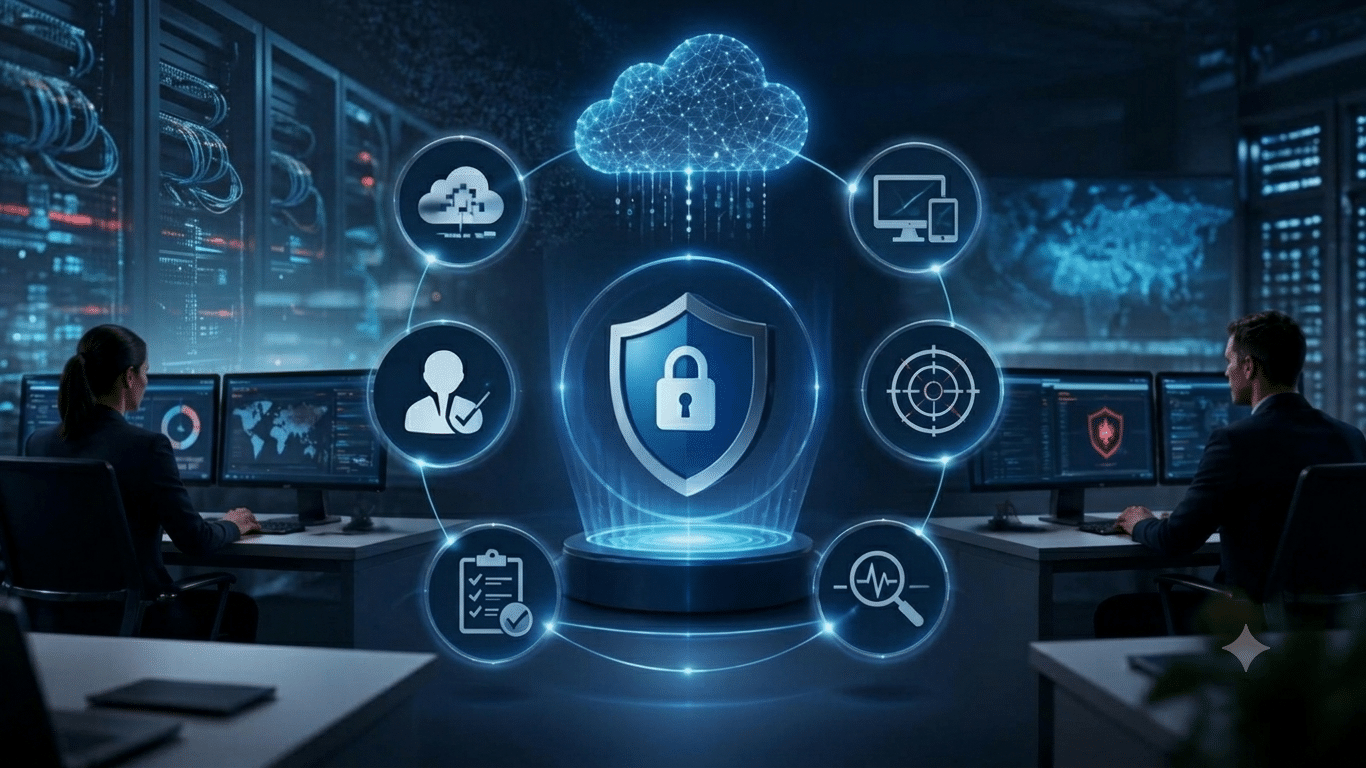
The assessment may examine areas such as:
- Identity and access management
- Microsoft 365 security
- Azure security configuration
- Endpoint protection
- Email security
- Data protection
- Security monitoring
- Threat detection
- Application access
- Device management
- Security policies
- Compliance controls
The final outcome should give decision makers a clearer picture of their current security position and the actions needed to improve it.
Identity and Access Management
Identity is one of the most important areas examined during a security assessment. If an attacker gains access to a legitimate account, traditional network defenses may not be enough to prevent unauthorized activity.
The assessment may review how users authenticate, how administrative accounts are protected, and whether access is appropriate for each employee. It may also examine inactive accounts, guest users, privileged accounts, authentication policies, and access management procedures.
Multi factor authentication is an important part of modern identity protection, but simply enabling it is not always enough. Organizations should consider which users have additional risk, how administrative accounts are protected, and whether authentication policies reflect the sensitivity of different resources.
Privileged access deserves particular attention because administrator accounts can provide access to critical systems and information. Strong controls around administrative identities can significantly reduce the potential impact of compromised credentials.
Microsoft 365 Security
Microsoft 365 is central to many organizations, which makes its security configuration an important part of an assessment. Email, files, collaboration tools, calendars, documents, and business communications may all operate within the environment.
The assessment can examine how Microsoft 365 services are configured and whether security policies are aligned with business requirements. Email protection, user access, external sharing, collaboration settings, and data protection may all require review.
Organizations should also examine how employees share documents with external users. A file that appears harmless may contain confidential information, and excessive sharing permissions can create unnecessary exposure.
Security should therefore be considered alongside productivity. The objective is not to prevent employees from collaborating but to ensure that collaboration happens within appropriate controls.
Azure Security
Organizations using Azure may have cloud resources supporting applications, databases, virtual machines, storage, analytics, and other services. A security assessment can examine how these resources are configured and whether access is properly controlled.
Cloud security requires attention to identity, network configuration, resource permissions, data protection, monitoring, and administrative access. Misconfigured resources can sometimes create significant exposure even when security tools are already deployed.
The assessment should also consider whether resources follow consistent security practices. As cloud environments grow, organizations can end up with different configurations across departments or projects. Standard policies and clear ownership can help reduce unnecessary variation.
Endpoint and Device Security
Employees access business systems through laptops, desktops, mobile devices, and other endpoints. If these devices are compromised, attackers may gain access to business accounts or sensitive information.
An assessment can examine whether company devices are properly managed, protected, updated, and monitored. It may also review whether employees are using personal devices and what controls apply to those devices.
Microsoft Intune can play an important role in device management for organizations using Microsoft technologies. Security teams may review device compliance, application management, configuration policies, and access requirements.
Endpoint security should not be treated as a separate issue from identity security. A secure account being accessed from an unmanaged or compromised device can still create risk.
Email and Collaboration Security
Email remains a common target for phishing, credential theft, malicious attachments, and social engineering. A security assessment should therefore examine how email threats are detected and how users are protected.
Security teams may review policies for suspicious messages, malicious links, attachments, external senders, and impersonation attempts. They may also examine how incidents are reported and investigated.
Collaboration platforms should receive similar attention. Teams, SharePoint, and other Microsoft 365 services allow employees to share information quickly, but that convenience can create security challenges when permissions and external access are not managed carefully.
Organizations should establish clear rules for external collaboration and regularly review whether those rules are being followed.
Data Protection and Information Security
Data is often the most valuable asset an organization needs to protect. Customer information, financial records, intellectual property, employee information, contracts, and business plans may all require different levels of protection.
A security assessment can examine where sensitive information is stored, who can access it, how it is shared, and whether appropriate protection policies are in place.
Data classification can help organizations understand which information requires stronger controls. Not every document needs the same level of protection, so businesses should identify their most sensitive information and establish appropriate policies.
Organizations should also consider what happens when an employee leaves. Access should be removed promptly, company information should remain protected, and ownership of important documents should be transferred appropriately.
Microsoft Defender and Threat Protection
Microsoft Defender technologies can provide protection across areas such as endpoints, identities, email, applications, and cloud environments. An assessment can examine whether relevant security capabilities are configured properly and whether alerts are being handled effectively.
Having a security product does not automatically mean that an organization is protected from every threat. Security teams need to understand what alerts are generated, who reviews them, how incidents are investigated, and what actions are taken.
An assessment can therefore examine both technical configuration and operational readiness. A security alert that remains unanswered for several days may create a very different risk from one that is investigated quickly by an experienced team.
Security Monitoring and Microsoft Sentinel
Organizations with more complex environments may need centralized security monitoring. Microsoft Sentinel can help collect and analyze security information across different sources.
An assessment may examine whether important security events are being collected, whether alerts are meaningful, and whether security teams have procedures for responding to incidents.
Monitoring should focus on useful information rather than generating an overwhelming number of alerts. Too many low value alerts can make it harder for security teams to identify genuine threats.
A mature monitoring strategy combines technology with clearly defined responsibilities and response procedures.
Compliance and Security Policies
Security assessments may also consider regulatory and organizational requirements. Businesses in healthcare, finance, government, and other regulated industries may have specific obligations regarding data protection, access, retention, and incident management.
Microsoft security technologies can support compliance objectives, but using Microsoft security products does not automatically make an organization compliant with every regulation.
Businesses need to understand their specific requirements and determine how technology, policies, employee behavior, documentation, and monitoring work together to satisfy those obligations.
Policies should also be reviewed periodically. A policy written several years ago may no longer reflect how employees work or how the organization uses cloud services.
Common Security Gaps an Assessment Can Reveal
A security assessment can uncover problems that may not be obvious during normal IT operations. Some organizations discover that security controls exist but are inconsistently configured.
Common findings can include:
- Excessive administrative privileges
- Inactive user accounts
- Weak authentication policies
- Unmanaged devices
- Excessive external sharing
- Outdated security configurations
- Incomplete monitoring
- Poor incident response procedures
- Inconsistent access permissions
- Unclear data ownership
- Missing security documentation
Not every finding has the same level of risk. Organizations should prioritize issues based on business impact, likelihood, exposure, and the importance of the affected system.
How to Prepare for a Microsoft Security Assessment
Preparation can make an assessment more productive. Organizations should first establish what they want to learn from the review.
The assessment may focus on a broad Microsoft environment or concentrate on a particular concern such as identity security, Microsoft 365, Azure, endpoint protection, or compliance.
Before the assessment begins, gather information about the current environment. This may include user accounts, administrator roles, Microsoft 365 services, Azure resources, endpoint management, security tools, policies, and known incidents.
It is also useful to identify recent technology changes. New cloud deployments, acquisitions, remote work changes, application migrations, or organizational restructuring can affect security requirements.
What Security Teams Should Have Ready
A prepared organization can provide relevant documentation and information without spending unnecessary time searching for basic details during the assessment.
Useful information may include:
- Current network and cloud architecture
- User and administrator information
- Security policies
- Device management information
- Existing security alerts
- Incident response procedures
- Compliance requirements
- Application inventories
- Data classifications
- Third party access information
The purpose is not to create paperwork for its own sake. Good documentation helps security teams understand how technology is actually being used and where responsibilities sit.
Prioritizing Assessment Findings
One of the most important stages comes after the assessment. A long list of security findings is not the same as a security improvement plan.
Organizations should categorize findings according to risk and business importance. Critical identity issues may need immediate attention, while lower risk configuration improvements can be included in a longer roadmap.
Each priority should ideally have an owner, an expected completion period, and a clear definition of what improvement looks like.
For example, if an assessment identifies excessive administrator privileges, the organization should not simply record the finding. It should determine which accounts require elevated access, remove unnecessary permissions, and establish a process for reviewing privileged access regularly.
Building a Long Term Security Improvement Plan
Security cannot be treated as a single project that ends when the assessment report is delivered. Technology environments change constantly, new employees join, applications are added, permissions change, and attackers develop new methods.
Organizations should use assessment findings to create an ongoing security improvement program. This can include regular identity reviews, device checks, security monitoring, policy updates, employee awareness training, and periodic reassessments.
The goal is to make security part of normal IT operations rather than something addressed only after an incident occurs.
How Cambay Solutions Can Support Microsoft Security Initiatives
Cambay Solutions can help organizations assess and improve Microsoft focused security environments by looking at identity, cloud infrastructure, Microsoft 365, endpoint management, security monitoring, compliance requirements, and related Microsoft technologies.
A security program often involves several connected services rather than one security product. Identity controls affect application access, endpoint security affects account protection, data policies affect collaboration, and monitoring affects incident response. Looking at these areas together can provide a clearer understanding of overall security requirements.
Cambay Solutions can also support organizations that need assistance with Microsoft security and compliance initiatives, Azure security, Microsoft 365 security, identity management, and broader cloud security planning. The focus should remain on identifying meaningful risks, prioritizing improvements, and establishing security practices that can be maintained over time.
FAQs
What is a Microsoft security assessment?
A Microsoft security assessment is a structured review of security controls across a Microsoft technology environment. It can examine identity, Microsoft 365, Azure, devices, data, applications, monitoring, policies, and compliance requirements.
Why should a business conduct a security assessment?
A security assessment can help identify weaknesses that may not be visible during normal IT operations. It gives organizations an opportunity to address security gaps before they contribute to a serious incident.
What does a Microsoft security assessment cover?
The scope depends on the organization, but it can include identity and access management, Microsoft 365, Azure, endpoint security, data protection, email security, monitoring, threat protection, and compliance controls.
How often should security assessments be performed?
The appropriate frequency depends on the organization’s risk profile, industry requirements, technology changes, and security maturity. Organizations should also reassess security after major cloud migrations, acquisitions, system changes, or significant incidents.
Is Microsoft security enough by itself?
Microsoft provides a broad range of security capabilities, but technology alone does not guarantee security. Effective protection also depends on proper configuration, access management, monitoring, policies, employee behavior, incident response, and ongoing maintenance.
How can a company prepare for a security assessment?
Start by defining the assessment objectives and scope. Gather relevant information about users, devices, applications, cloud resources, security policies, compliance requirements, and known security concerns.
What happens after a security assessment?
The findings should be reviewed and prioritized according to business risk. Organizations can then create an improvement plan with clear owners, timelines, and measurable outcomes.
Can a security assessment improve compliance?
It can help identify gaps between current security practices and organizational or regulatory requirements. However, compliance depends on the specific regulation and requires more than technology configuration alone.
Does a security assessment only focus on technical issues?
No. A useful assessment can also examine policies, procedures, responsibilities, employee practices, access governance, incident response, and other operational areas.
Turning Assessment Findings Into Better Security
A microsoft security assessment is most valuable when it leads to practical improvement rather than becoming another report stored and forgotten. The assessment should help an organization understand where it is exposed, which issues matter most, and what actions can reduce those risks.
The strongest preparation starts with visibility. Organizations need to understand their identities, devices, applications, data, cloud resources, and security processes before they can determine whether those areas are adequately protected. Once the current environment is understood, security teams can prioritize improvements according to actual business risk.
Microsoft security capabilities can provide a strong foundation, but successful protection depends on how those capabilities are implemented and maintained. Regular reviews, appropriate access controls, effective monitoring, employee awareness, clear policies, and continuous improvement all contribute to a stronger security program.
For organizations operating increasingly through Microsoft cloud and productivity services, making security assessment part of regular technology planning can help reduce surprises and create a more controlled approach to managing cyber risk.